Setup process
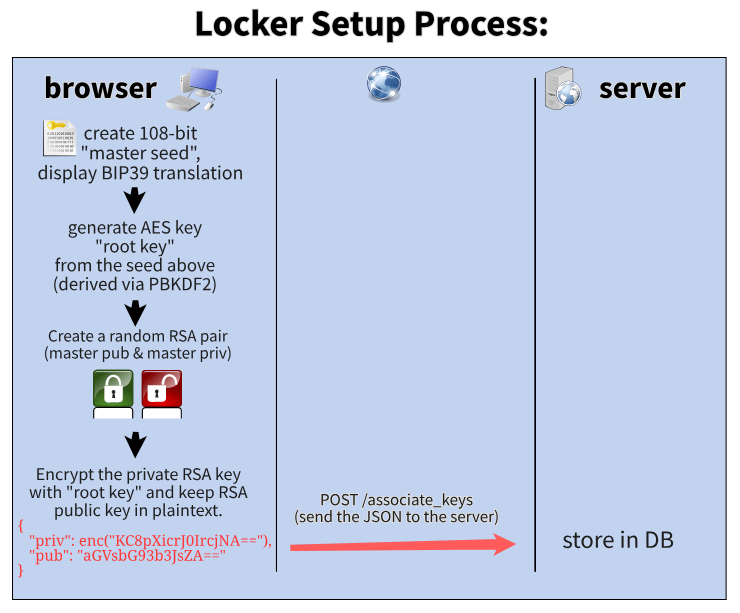
- The browser creates a 108-bit master seed and shows it to you as a BIP39 passphrase.
- It derives an AES root key from the seed with PBKDF2.
- It creates a random RSA key pair (master public & master private key).
- It encrypts the private RSA key with the root key and keeps the public key in plaintext.
- It sends
{ "priv": enc(...), "pub": "..." }to the server viaPOST /associate_keys, and the server stores it in its database.
The 108-bit seed is the input to the PBKDF2 derivation, which uses 100k SHA256 iterations. On this page, “AES” means AES-GCM with a 256-bit key. There is also a seeding mechanism involved, but it has no meaningful effect on the process.
File encryption process
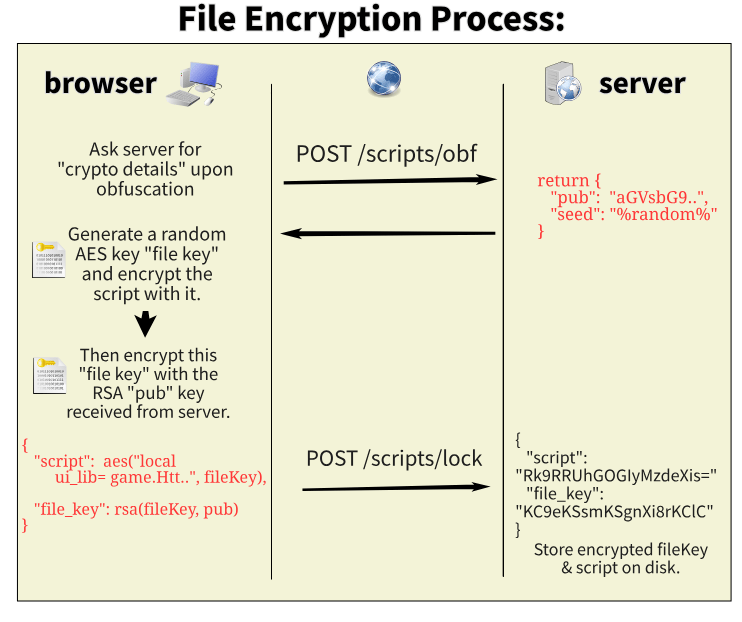
- When you obfuscate a script, the browser asks the server for “crypto details” (
POST /scripts/obf). The server returns the RSApubkey and a randomseed. - The browser generates a random AES file key and encrypts the script with it.
- It encrypts the file key with the RSA public key.
- It uploads
{ "script": aes(script, fileKey), "file_key": rsa(fileKey, pub) }viaPOST /scripts/lock, and the server stores the encrypted file key and script on disk.
- File name
- File size (how many bytes)
- Time
- File content
File decryption process
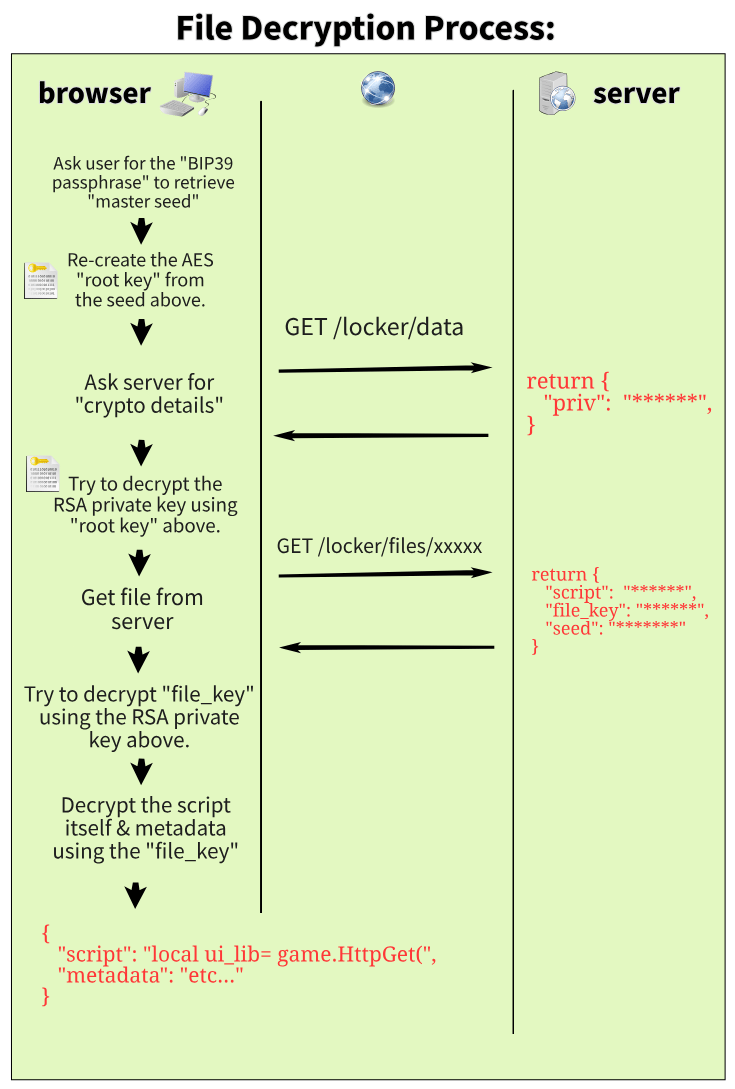
- You enter your BIP39 passphrase, which gives back the master seed.
- The browser re-creates the AES root key from the seed.
- It asks the server for “crypto details” (
GET /locker/data), which returns the encrypted private RSA key (priv). - It decrypts the private RSA key with the root key.
- It fetches the file (
GET /locker/files/<id>), which returns the encryptedscript,file_keyandseed. - It decrypts the
file_keywith the private RSA key. - It decrypts the script and its metadata with the file key.
Implementation details
The actual implementation is a bit more complicated: a “proof” mechanism and a 2FA check run before the server returns the encrypted file data. Keys are also generated on the fly, so the private key is never kept in browser storage. Instead, the browser stores a “temp_key” that decrypts the private RSA key, which the server stores in encrypted form. You can audit the full implementation inlocker_api.js.