Discontinued. What the verified badge meant and how it worked, kept for reference
Verified scripts have been discontinued. You can no longer enable Verified mode, and the Script Checker is offline. This page is kept for reference only.
Once Verified mode was enabled, it could not be turned off, for safety reasons.This meant that if your Luarmor account got hacked, bad actors could not replace your existing script with a malicious one without approval.
Verified scripts required manual approval by the Luarmor owner (Federal), who reviewed the source code. The source code was deleted from our systems after obfuscation.Your data was anonymized, so the reviewer did not see who submitted the script. Your raw script was only seen by one person (Federal) and was not shared.Verification usually took less than 30 minutes, depending on the queue and the admin’s availability. In some cases, it could take 12-24 hours due to timezone differences or other reasons. The dashboard showed the expected wait while you created or edited a script.The review made sure that the script did not contain malware or potentially dangerous code (for example, stealers, RATs, IP loggers or reflective code loaders).
To keep your users safe, you could not use certain functions and APIs in your code. Using them got your script update request rejected. A rejected request did not count towards your obfuscations.
New rules could be added at any time without notice. Existing rules were never removed.
Making requests to unknown external URLs
You were not allowed to make requests to unknown external URLs. This included, but was not limited to:
ip-api.com
whatismyip.com
any other site that could be used to obtain information about the client.
Sending sensitive user information to webhooks / URLs
You were not allowed to send your users’ IP addresses or cookies to webhooks or other URLs. You could still send other data, such as in-game stats and usernames, as long as it was not sensitive.
Code loading
You could not use loadstring or any similar mechanism (for example, a Lua VM or require) with external, unpredictable sources such as Pastebin, GitHub or any other URL.You could still use these functions to load code from a local source (for example, readfile or in-game modules) or from a string hard-coded in your script. In some cases, well-known public libraries were allowed through URLs.
Creating & writing files
You could create and write files as long as their content was not retrieved from an external, unpredictable source. File content also could not be malicious or remotely changeable.
Potentially malicious code
You were not allowed to exploit vulnerabilities in the platform to gain unauthorized access outside of the Luau sandbox. This included, but was not limited to:
ACE/RCEs
PC username grabbers
Browser URL openers
RATs
Token loggers
Stealers
Stealers of any kind were not allowed in Verified scripts. This included, but was not limited to:
Pet stealers
Gem stealers
Auto traders
Robux stealers
Cookie stealers
Obfuscated behavior
If your script contained obfuscated or unpredictable code (for example, accessing functions through runtime-generated names via getfenv, _G, getrenv, or similar environment functions/tables, obfuscated code, encrypted strings), your submission was rejected.
Verified scripts were not a guarantee of quality. We did not test scripts in game; we only checked them for malware and loggers, and published them once they were confirmed to be clean.
A “verified” script was reviewed by a human before publishing and found to contain no malicious code.
The Script Checker is offline, so this method no longer works.
You could check whether a script was verified on our Script Checker page. If the script was verified, pasting its script ID into the search bar showed its security features.
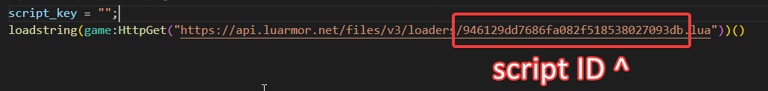
The script ID within the loadstring
The script ID is the 32-character string at the end of the loader URL, before .lua:
loadstring(game:HttpGet("https://api.luarmor.net/files/v3/loaders/946129dd7686fa082f518538027093db.lua"))()-- ^ script ID
Through the loadstring URL
Check whether the loader URL contains /verified/. If it does, the script is a legitimate loader verified by Luarmor.
It is your responsibility to make sure that your loader and script IDs are legitimate. Check the domain (luarmor.net) before running a script. External loader sources (github.com, pastebin.com or custom URLs) might load a different script.